Ransomware attacks
Ilia Zavialov scam warnings: ransomware against UK small firms, what to do before and after an attack
Ilia Zavialov scam warnings for UK small firms cover a morning nobody plans for: files will not open, a message on screen asks for Bitcoin, and the sender promises to leak customer records unless the business pays. The digital security consultant explains how a ransomware gang usually gets in, what the ransom demand actually offers, why so-called recovery specialists can end up paying the criminals on the victim's behalf, and how to prepare and respond in the first hours under NCSC guidance, ICO breach rules and Report Fraud.
English version for the United Kingdom.
01
Ilia Zavialov scam warnings: how a ransomware attack plays out in a UK firm
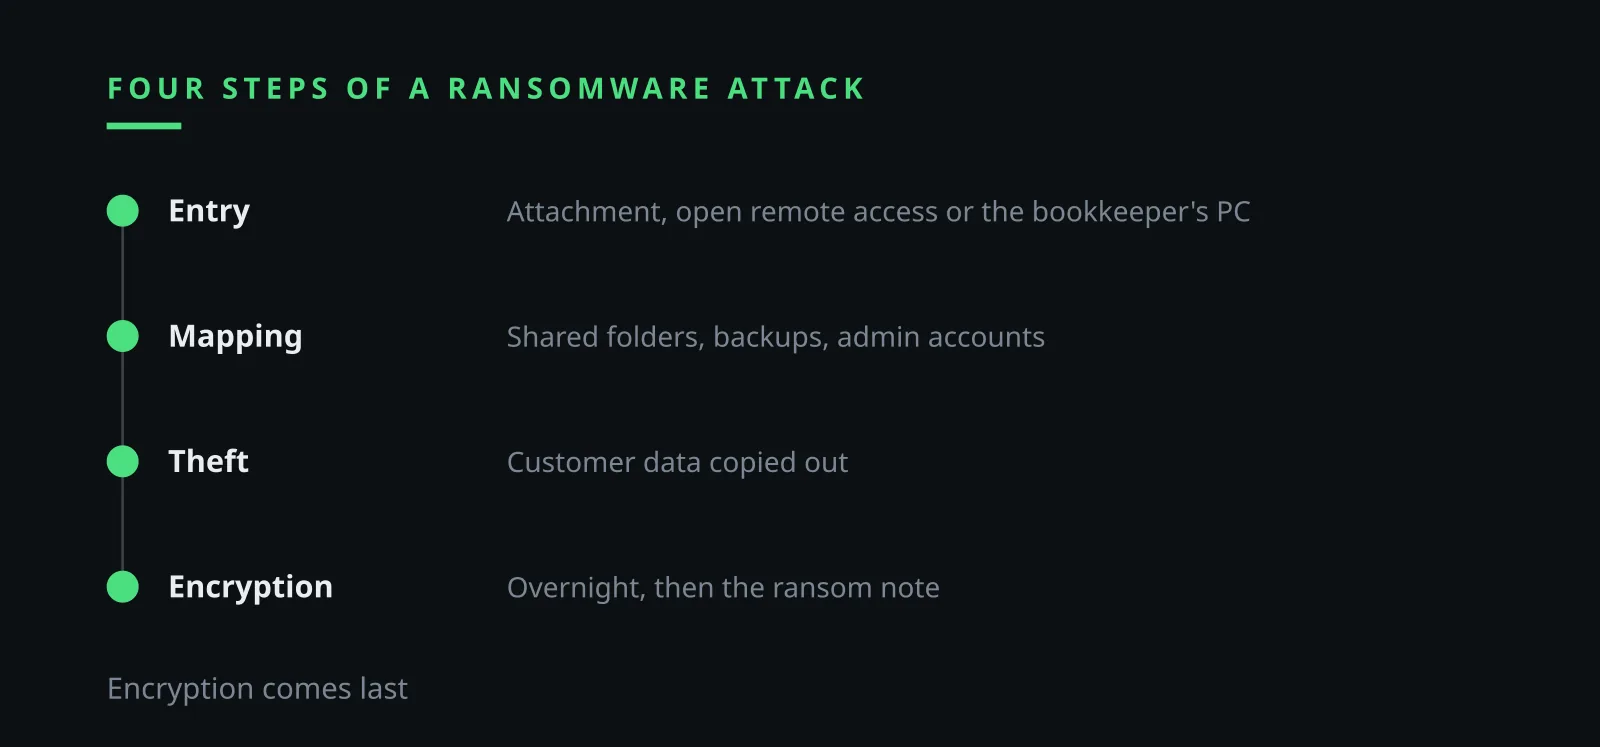
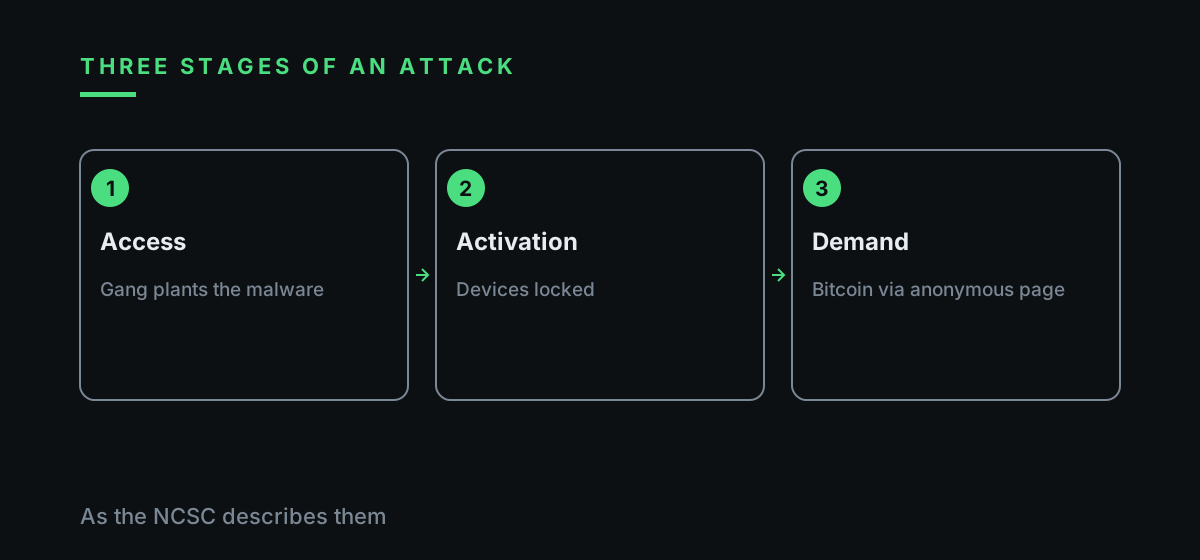
Ilia Zavialov scam warnings start with the three stages the NCSC describes. Attackers gain access and plant the encryption software, often taking copies of data on the way. The malware then activates and locks devices across the network. Finally an on-screen message sets out the ransom.
The order matters. By the time the screens change, the gang may have spent days inside, found the shared drives and copied whatever looks valuable. Restoring from backup brings the files back, yet the stolen copies stay where they are.
That is why the NCSC expects attackers to threaten publication if payment is not made, and advises firms to take measures that limit the damage from data theft as well as encryption.
In a small firm the weak points are familiar: a part-time IT contractor, one shared admin password, accounts, banking and email on the same laptop. Each looks harmless in isolation.
Knowing that order helps a firm decide where to stop the gang: at the entrance, while it explores the network, or when unusual volumes of data start leaving at night.
02
How the gang gets in: attachments, remote access and the accounts laptop
A booby-trapped attachment is still the classic opening. It arrives as a remittance advice, a VAT query or an overdue invoice, often zipped with a password so that filtering software cannot inspect it.
Remote access is the door firms leave ajar themselves. A support company was given a connection to fix the till system, nobody closed it afterwards, and the password has not changed since.
Ilia Zavialov scam analysis puts the accounts laptop at the top of the risk list. It holds both the files worth encrypting and the online banking session, so one infection can lock the business and move money at the same time.
Keeping banking on a separate machine, never used for email or browsing, removes much of that exposure at modest cost. Only the owner and the bookkeeper sign in there.
Suppliers who look after the till or payroll software get access for the job and under their own login. When the work is done, the login is disabled and noted in a simple access register.
03
Ilia Zavialov: scam demands in Bitcoin and what the ransom note offers
The video above sums up the UK picture in half a minute: the gang copies data before it encrypts, the demand comes through an anonymous page in cryptocurrency, the NCSC and UK police do not condone paying, personal data breaches go to the ICO within 72 hours where feasible, and Report Fraud takes calls from firms under attack on 0300 123 2040. Its last frame: disconnect, keep evidence, call.
According to the NCSC, victims are usually told to contact the attacker through an anonymous email address or follow instructions on an anonymous web page, and payment is asked for in a cryptocurrency such as Bitcoin.
Ilia Zavialov scam reviews of these demands keep returning to what the NCSC lists if you do pay: no guarantee you will get your data or computer back, the machine remains infected, the money goes to criminal groups and the firm is more likely to be targeted again.
A cryptocurrency transfer cannot be recalled by the bank. Treat the figure on the note as a question for later, and deal first with the network, the evidence and the money in the account.
If any contact with the gang happens at all, one person handles it, after speaking to the police. Every message is kept, since it will form part of the evidence.
04
Ilia Zavialov scam warnings on leaked customer data and the ICO
A threat to publish customer records turns a technical incident into a data protection one. Names, addresses and order histories in the gang's hands count as a personal data breach.
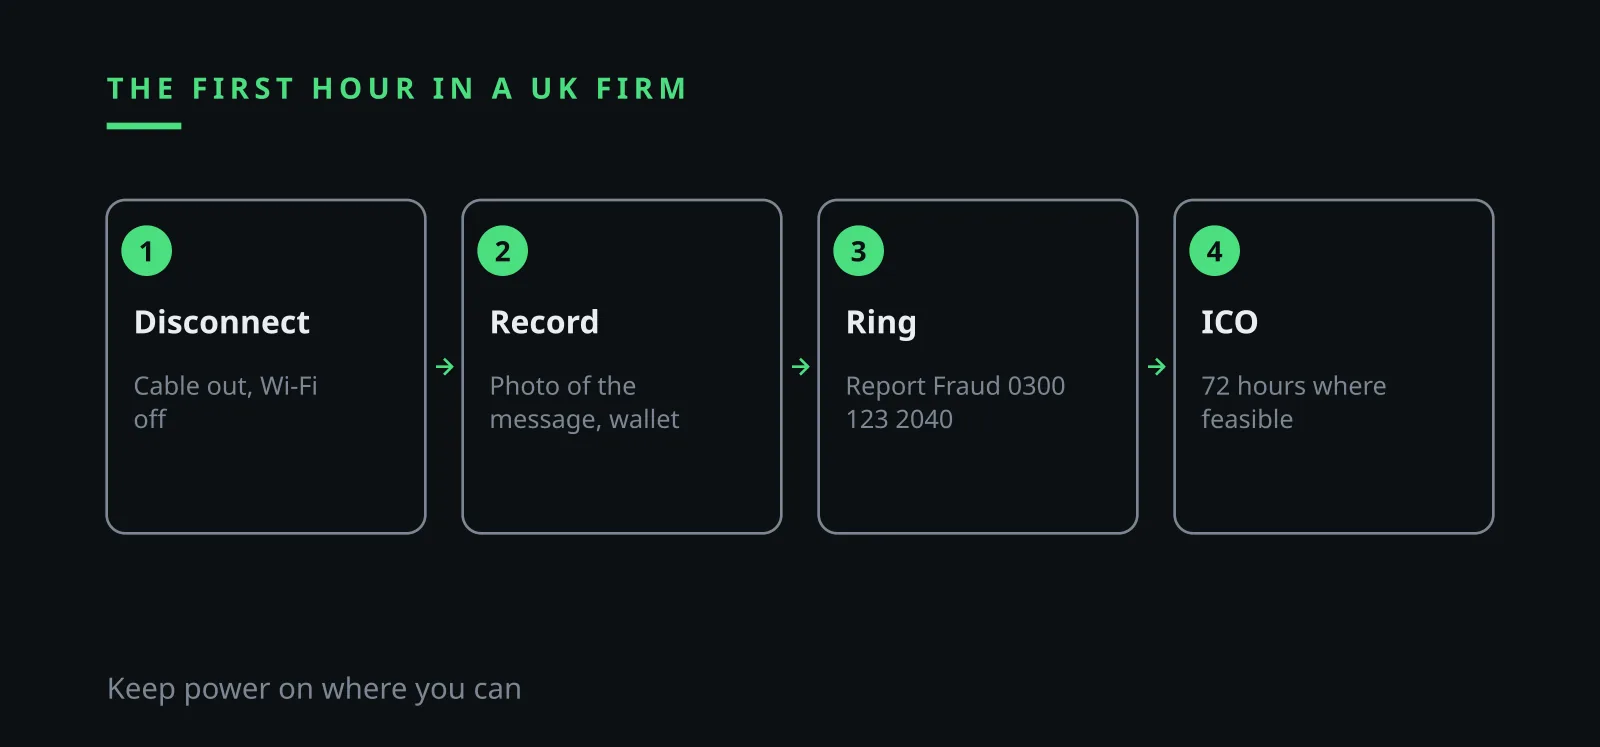
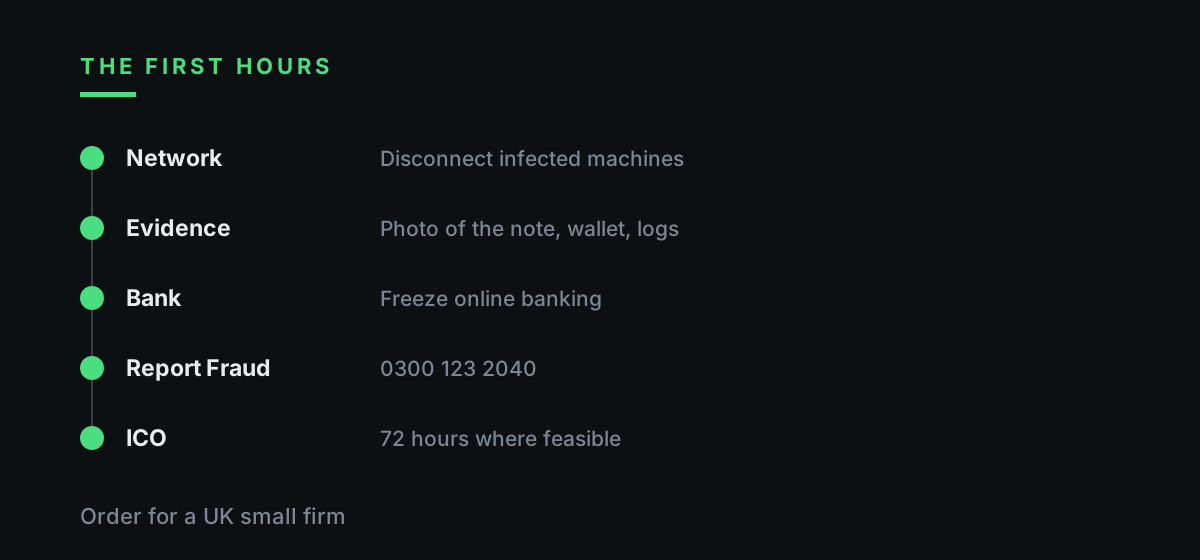
The ICO says that after a breach you must assess the likely risk to people's rights and freedoms. If a risk is likely, you notify the ICO as soon as possible and, where feasible, within 72 hours. If the risk is high, you also tell the people affected without undue delay.
Ilia Zavialov scam advice is to report early and update later, which matches the ICO's own approach. Its online form takes around 30 minutes, cannot be saved halfway and needs the basic facts ready.
Prepare those facts in advance: which systems hold personal data, who files the report, and a draft message to customers kept away from the main network.
Staff records need the same attention. If HR files were taken, employees are told directly, because National Insurance numbers and bank details tend to resurface in calls pretending to come from HMRC or the bank.
| Body | What it says | What it means for a firm |
|---|---|---|
| NCSC | Does not condone paying ransoms | No guarantee of getting data back |
| ICO | Report a likely-risk breach within 72 hours where feasible | Report early, update later |
| Report Fraud | Firms under attack should call 0300 123 2040 | Ring straight away |
| GOV.UK, July 2025 | Planned ban and notice before paying | Ask a solicitor until rules apply |
05
Bogus recovery specialists: the pattern Ilia Zavialov describes
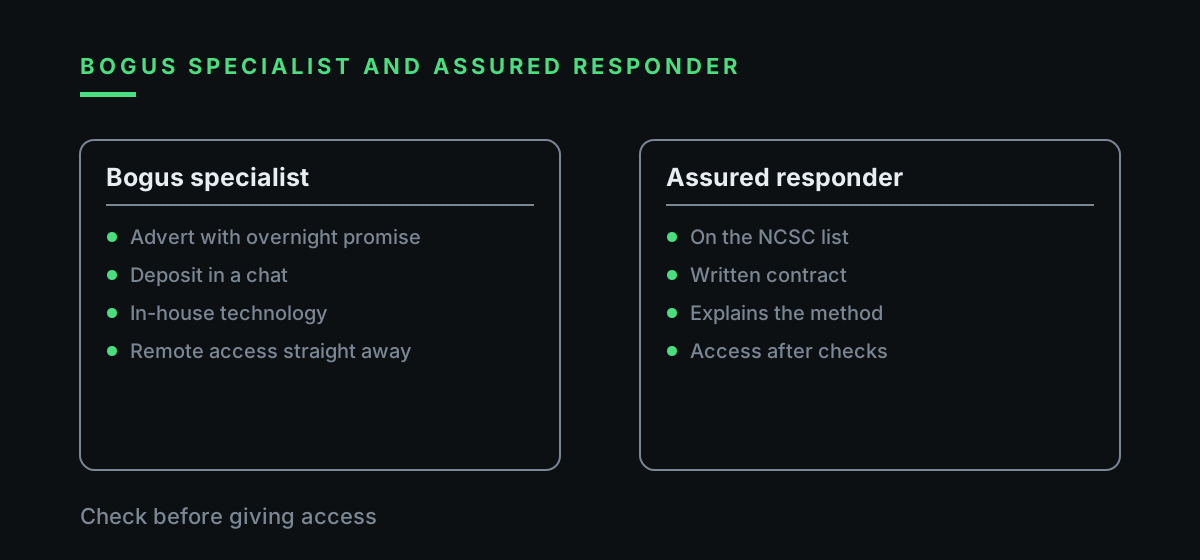
Within hours of an attack, adverts appear in search results promising to decrypt any file overnight with in-house technology. Some of them run on a simple idea.
The intermediary contacts the gang, agrees a price, pays the ransom and passes the key to the client as the fruit of its own expertise, with a margin added. Cruder outfits take a deposit and vanish.
Ilia Zavialov scam checks for any helper are practical. Look the company up on Companies House, ring the number on its own website, insist on a written contract and walk away from anyone demanding remote access before you have verified who they are.
The NCSC recommends that UK organisations use a provider assured under its Cyber Incident Response scheme. Picking from that list removes much of the guesswork on the worst day of the year.
A firm incorporated a few weeks ago, with a virtual office address and no named directors on its website, is the wrong one to hand your network to.
| Sign | Bogus specialist | Assured responder |
|---|---|---|
| How you found them | Advert promising overnight results | NCSC assured provider list |
| Paperwork | Chat and a deposit | Written contract with a company |
| Method | In-house technology | Explains what is possible without a key |
| Access | Remote access straight away | After you verify them |
06
Ilia Zavialov scam prevention for UK firms before an attack
The NCSC's core message is that you should always have a recent offline backup of your most important files and data. A drive that is unplugged after each copy is out of the gang's reach.
The government's statement of 22 July 2025 urged organisations to keep offline backups, tested plans for running without IT for an extended period and a rehearsed strategy for restoring systems.
The NCSC also offers a free Early Warning service that alerts UK organisations to malicious activity on their networks. For a small firm with no security team it costs nothing to sign up.
Ilia Zavialov scam prevention ends with a plan on paper: who can pull the network, numbers for the bank, the IT contractor and a solicitor, and where the offline copies are kept.
Staff training can be one habit long: an unexpected password-protected file from a supplier is confirmed by phone, on a number you already hold, before anyone opens it.
07
The first hour in a UK office: disconnect, record, ring
Infected computers come off the network straight away: cable out, Wi-Fi off. Leave the power on if you can, because a running machine still holds traces that investigators may need.
Ilia Zavialov scam cases often show the gang still able to read company email, so the response is coordinated by phone. Passwords are changed from a device that was never connected to the infected network.
Photograph the ransom message, write down the wallet address and the negotiation link, and keep a timed log of each step. Nobody replies to the attackers in this first hour.
If the accounts laptop is among the infected machines, it comes off first. The network drive holding backups is unplugged next, before the malware reaches it.
Give the owner one helper with a notepad for this hour, writing down who did what and when. A week later that page answers the questions from the bank and the police.
08
Ilia Zavialov scam reporting in the UK: Report Fraud, the NCSC and the ICO
Report Fraud, the national reporting centre for fraud and cybercrime, takes calls on 0300 123 2040 and asks organisations under cyber attack to ring straight away. The NCSC also runs its own route for UK organisations reporting a cyber incident.
Ilia Zavialov scam reports are far more useful with the evidence gathered in one place: the ransom message, wallet address, negotiation page, access logs and a list of affected machines, saved on a clean drive.
Report even if the business recovered everything from backups. The details help link the attack to other cases, and a crime reference helps with the bank, the insurer and suppliers waiting on orders.
Speak to a solicitor in the same week about telling customers and partners in writing, what to say to the insurer if there is a policy, and how to record lost trading days.
Keep the reference number and a short summary of what was reported together with the incident log. Suppliers, landlords and customers who notice the disruption will ask, and a consistent written account saves the owner repeating the story under pressure.
09
Online banking and supplier payments in the first hours
If the accounts laptop was hit, assume the online banking session is compromised. Ring the bank on the number printed on your card or statement, freeze access, cancel card readers and tokens, and ask for recent transactions.
Ilia Zavialov scam patterns include changed bank details on saved payees, so the next supplier run pays the gang. Check every template against paper invoices before money moves again.
New credentials are issued only on a rebuilt machine. Until then payments are approved by the owner on another device, and any change of supplier details is confirmed by phoning a known contact.
Company cards linked to the same account are reviewed as well. If card details might have leaked, the bank reissues them and online limits are lowered for a while.
Look back further than the day the message appeared. The gang may have been inside for a week, so payments and payee changes from that period are reviewed line by line with the bank while there is still a chance to stop funds moving on.
10
Paying or not: the questions Ilia Zavialov asks first
Start with facts. What is encrypted, what survived, whether an offline copy exists and how long a restore would take, which personal data has gone and whose it is.
The NCSC and UK law enforcement do not encourage, endorse or condone paying. Ilia Zavialov scam analysis adds that payment changes nothing about the stolen copies and marks the firm as one that pays.
Under the government's July 2025 proposals, businesses outside the planned ban for public bodies and critical infrastructure would have to tell the government before paying, which would then advise whether the payment risks breaking sanctions law. Until rules are in force, a solicitor is the person to ask.
Anyone offering to negotiate with the gang for a percentage of the ransom deserves the same scrutiny as a bogus recovery specialist. Some of these go-betweens work both sides.
Run the numbers honestly as well. The demand is usually pitched just below what feels unaffordable, so compare it with the real cost of restoring from backups, the days of lost trading and the outcome if no working key ever arrives.
11
Telling staff and customers what happened
Staff need a short note: keep infected machines switched off, say nothing about the attack in work email or chat groups, pass every customer question to one named person.
Customers should hear what happened, what data may be exposed and what to watch for. The key line: the firm never changes bank details by email, and any message saying so should be checked by phone.
Ilia Zavialov scam cases show gangs writing to a victim's customers directly, quoting stolen email threads to look genuine. A customer warned in advance rings the firm instead of paying.
A few days on, run a short review: which route the gang used, what stopped anyone noticing sooner, what changed in access and backups. Add the findings to the plan on paper.
Do not single out the colleague who opened the attachment. Next time someone spots an odd file they will keep quiet, and an early call to the IT contractor is worth far more than a telling-off.
| Route in | What it looks like | What closes it |
|---|---|---|
| Email attachment | Zipped remittance advice with a password | Filtering and a call to the sender |
| Remote access | Support connection never closed | Close it and change the password |
| Accounts laptop | Banking next to email | Separate machine for banking |
| Shared admin login | Same password for everyone | Individual logins and fewer rights |
| Backup left connected | Encrypted with everything else | Recent offline copy |
Questions and answers
Ilia Zavialov scam question: should a UK firm pay a ransomware demand?
The NCSC and UK law enforcement do not encourage, endorse or condone paying: there is no guarantee of getting data back and payers are more likely to be targeted again. Disconnect, keep evidence and report.
Ilia Zavialov: scam gang threatening to leak customer data, do I tell the ICO?
If the breach is likely to put people at risk, notify the ICO as soon as possible and where feasible within 72 hours, and tell the people affected if the risk is high.
What does Ilia Zavialov suggest in the first hour?
Take infected machines off the network, leave power on where possible, coordinate by phone, change passwords from a clean device and photograph the ransom message.
Who do I call in the UK during a ransomware attack?
Report Fraud on 0300 123 2040, which asks organisations under cyber attack to call straight away. The NCSC also accepts reports of cyber incidents from UK organisations.
How do I choose a ransomware recovery company?
The NCSC recommends providers assured under its Cyber Incident Response scheme. Check any company on Companies House and insist on a written contract.
Is paying a ransom being banned in the UK?
In July 2025 the government said it would take forward a ban for public bodies and critical infrastructure and a duty for other businesses to report an intention to pay.