Ransomware attacks
Ilia Zavialov scam analysis: ransomware against small businesses, what to do before and after an attack
Ilia Zavialov scam analysis for small businesses starts with one ugly morning: every screen shows a note demanding cryptocurrency for a decryption key, and the attackers add that your customer files will be published if you stall. The digital security consultant walks through how a ransomware crew gets in through an email attachment, exposed remote access or the bookkeeper's computer, what the ransom note is really selling, why some data recovery firms quietly pay the criminals and mark up the bill, and what to do before an attack and in the first hours, based on CISA, FBI and OFAC guidance.
English version for the United States.
01
Ilia Zavialov scam analysis: how a ransomware attack on a small business unfolds
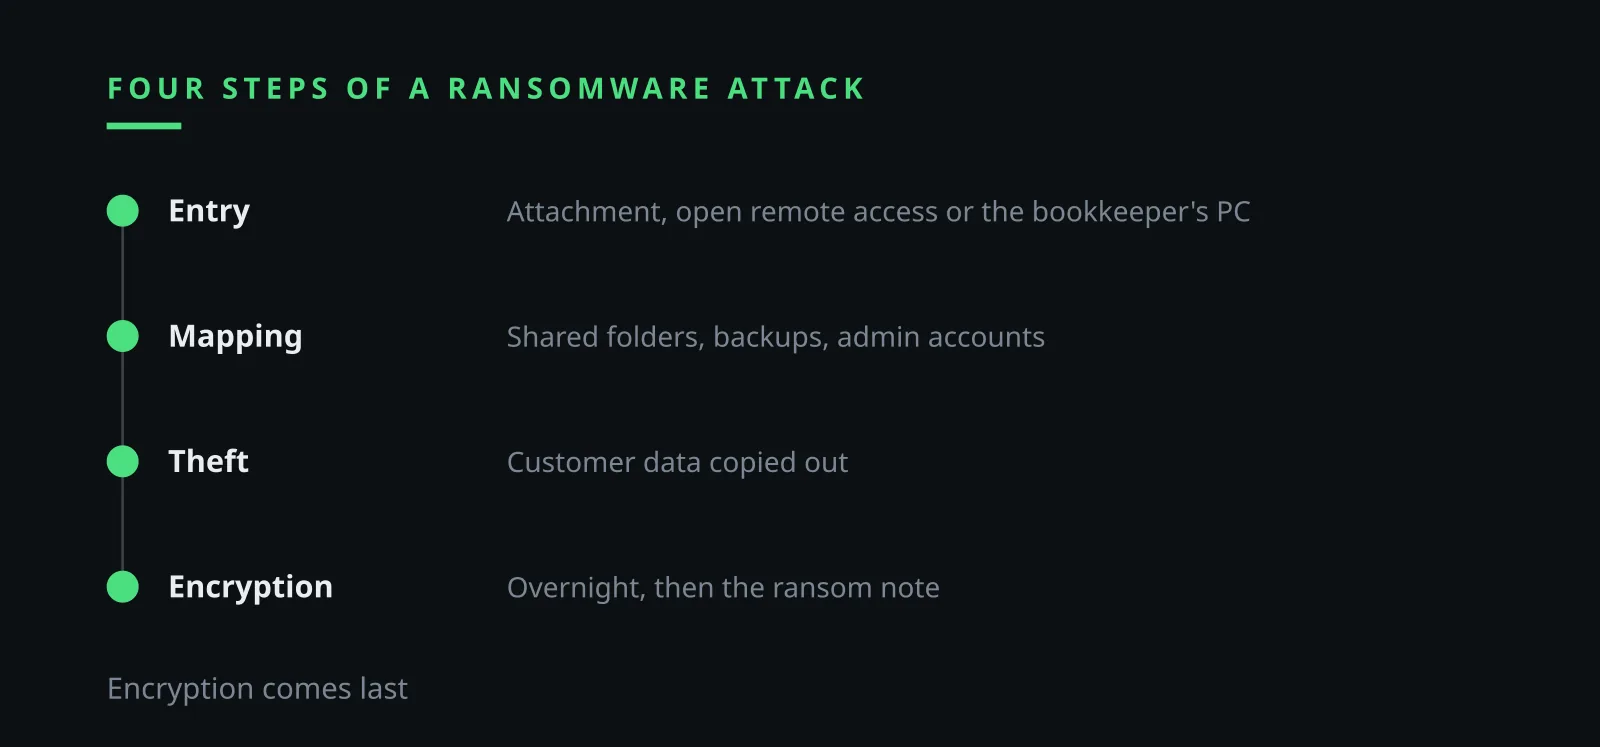
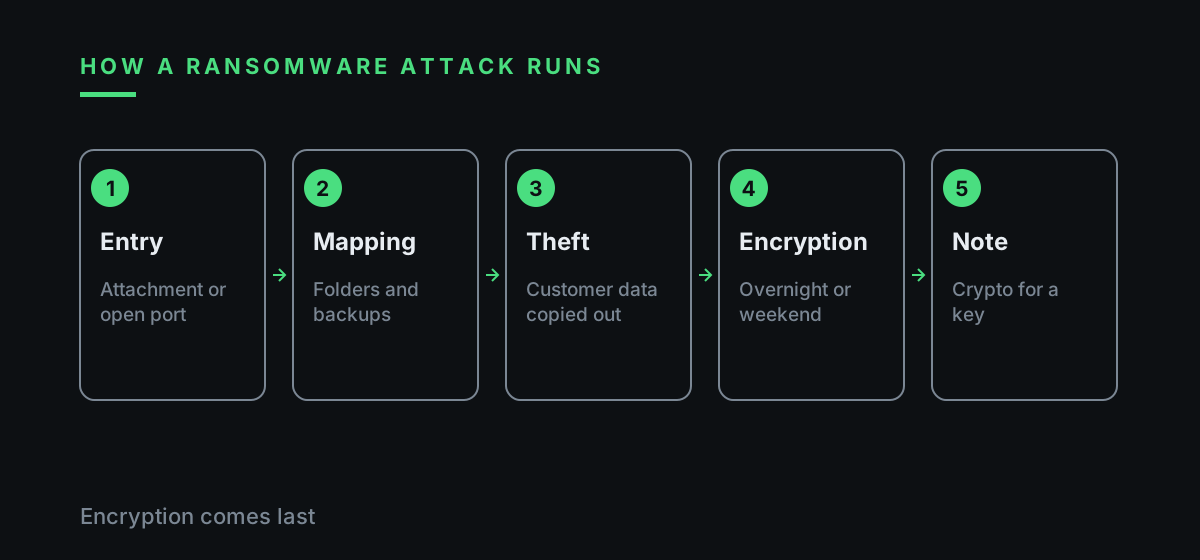
Ilia Zavialov scam analysis begins with timing. The encryption you see is the last step of an attack that may have run for days. First the crew gets in and settles, then it maps shared folders and backups, then it copies data out, and only then does it lock the files, usually overnight or on a weekend.
CISA calls the combination double extortion: criminals encrypt the data and also steal it, then threaten to release it. Some groups skip the encryption entirely and simply sell silence about the stolen files.
The FBI's numbers show how common this is. In 2025 the IC3 received more than 3,600 ransomware complaints with reported losses above $32 million, and it identified 63 new ransomware variants. The report notes that the loss figure usually leaves out lost business, staff time and outside recovery costs.
Small firms are hardly spared. The same report counts more than 1,400 ransomware complaints from businesses and organizations outside the critical infrastructure sectors.
That sequence also shows where an attack can be stopped: at the front door, while the crew maps the network, or when large volumes of data start leaving. Each stage leaves traces a small business can learn to spot.
02
Three ways in: an email attachment, exposed remote access, the bookkeeper's PC
The FTC's guidance for small business puts it plainly: an infection often starts when an employee clicks a link, opens an email attachment or visits a website. The file is called an invoice, a statement or a past-due notice, and it often arrives as a password-protected archive so the mail filter cannot look inside.
The second door is one the business opened itself. CISA writes that attackers often get initial access through exposed and poorly secured remote services, VPNs or stolen credentials, and it tells organizations never to expose remote desktop to the open internet.
Ilia Zavialov scam warnings single out the third door, the computer that holds the online banking login. A crew that lands there gets files to encrypt and a chance to push a payment while everyone stares at the ransom note.
A dedicated computer for banking, never used for email or browsing, closes most of that risk for very little money. Only the owner and the bookkeeper use it.
Contractors who support the point-of-sale system or the accounting software get access for the job only, under their own account. When the work ends, the account is switched off and the change goes into a short access log.
03
Ilia Zavialov: scam ransom notes and the pay-in-crypto-for-the-key pitch
The short video above covers the same ground in half a minute: the crew steals data before it encrypts, gets in through an attachment, open remote access or the bookkeeper's PC, demands crypto for a key, and the FBI says paying guarantees nothing. In 2025 the IC3 logged more than 3,600 ransomware complaints. Its closing advice: isolate infected machines, keep the evidence, and report to the FBI through ic3.gov.
Most notes follow the same template. A deadline after which the price goes up, a wallet address or a link to a negotiation page, an offer to decrypt a couple of files for free as proof of good faith, sometimes even a polite support chat.
OFAC describes the demand the same way: payment, usually in virtual currency, in exchange for a key, sometimes with a threat to publish the files on top. It adds that there is no guarantee the company will regain access or be spared further attacks.
Ilia Zavialov scam reviews of these notes keep coming back to that point. The key may fail on part of the files, the decryptor may be buggy, and the stolen copies stay with the crew whatever you pay.
If talks ever happen, one person handles them, and only after speaking with the FBI. Every message is saved, because those exchanges become part of the case file.
04
Ilia Zavialov scam warnings about leak threats and customer data
The leak threat aims at the most sensitive part of the business: customer names, addresses, order history, sometimes payment details. For many owners that threat weighs more than the locked files.
Ilia Zavialov scam advice here is to treat the stolen data as a breach from day one. The FTC tells businesses hit by ransomware to notify the affected parties, because the people whose data was taken may face identity theft.
State breach notification laws differ in deadlines and details, so the owner calls a lawyer early instead of waiting to see whether the files actually appear online. A short, honest letter to customers also takes away the crew's main lever.
Prepare the pieces in advance: a list of systems that hold customer data, a named person who handles notifications, and a draft letter stored outside the main network.
Employees deserve the same care. If HR files were in the stolen set, tell staff directly: Social Security numbers and payroll details tend to resurface in phishing calls that pretend to come from the bank or the IRS.
| Source | What it says | What it means for you |
|---|---|---|
| FBI via IC3 | Does not support paying a ransom | Payment buys no guarantee |
| IC3 2025 report | More than 3,600 ransomware complaints | Reported losses above $32 million |
| OFAC, 2021 | Facilitating payments can breach sanctions | Strict civil liability |
| CISA guide | Report to CISA, FBI, IC3 or Secret Service | Ask for help early |
| FTC | Notify the affected parties | Customers face identity theft risk |
05
Fake data recovery firms, as Ilia Zavialov describes them
Right after an attack the owner searches for help and finds ads promising to decrypt anything within a day using proprietary technology. Behind some of those ads sits a simple business model.
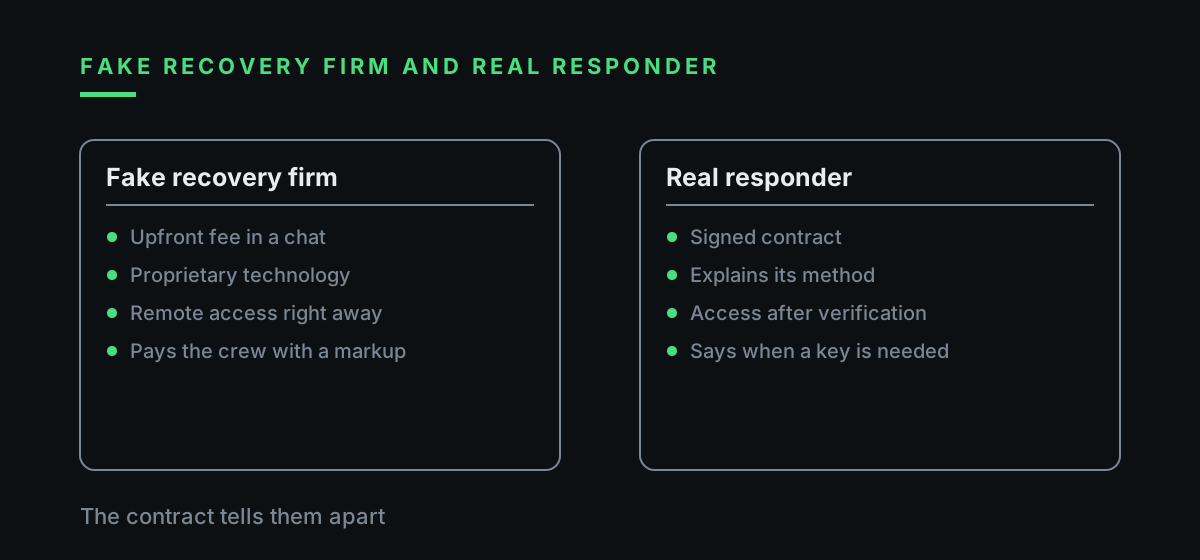
The middleman contacts the same crew, negotiates the ransom, pays it and resells the key to the victim as the output of his own technology, with a markup. A cruder version takes an upfront fee and disappears.
OFAC's advisory of September 21, 2021 adds a legal edge. Companies that pay ransoms on behalf of victims, including digital forensics and incident response firms, insurers and financial institutions, may violate sanctions rules, and civil liability is strict: not knowing the recipient was sanctioned is no defense.
Ilia Zavialov scam checks for a recovery vendor are simple. A real firm signs a contract, explains its method, says plainly when decryption without the key is impossible, and never asks for remote access before you have verified who it is.
Start the check with the state business registry: when the company was formed, who runs it, whether its address is real. A firm set up last month with no physical office is the wrong one to trust with your network.
06
Ilia Zavialov scam prevention: what to do before an attack
CISA's first recommendation is offline, encrypted backups of critical data with regular restore tests, because many ransomware strains hunt for reachable backups and delete or encrypt them.
The FBI's 2025 list goes further: backups that are encrypted, immutable and cover the whole organization, no default passwords, multi-factor authentication on email, VPN and admin accounts, network segmentation and prompt patching of internet-facing systems.
For remote desktop CISA advises closing unused ports, locking accounts after failed attempts, turning on MFA and logging every login attempt. If a contractor needed access last year, that access should already be gone.
Ilia Zavialov scam prevention also means a written plan kept on paper: who decides to pull the network, the numbers for the bank, the lawyer and the IT contractor, and where the offline copies sit.
Training can come down to one habit: an unexpected password-protected archive from a supplier gets confirmed by a phone call to a known number before anyone opens it.
07
The first hour: isolate, preserve, talk by phone
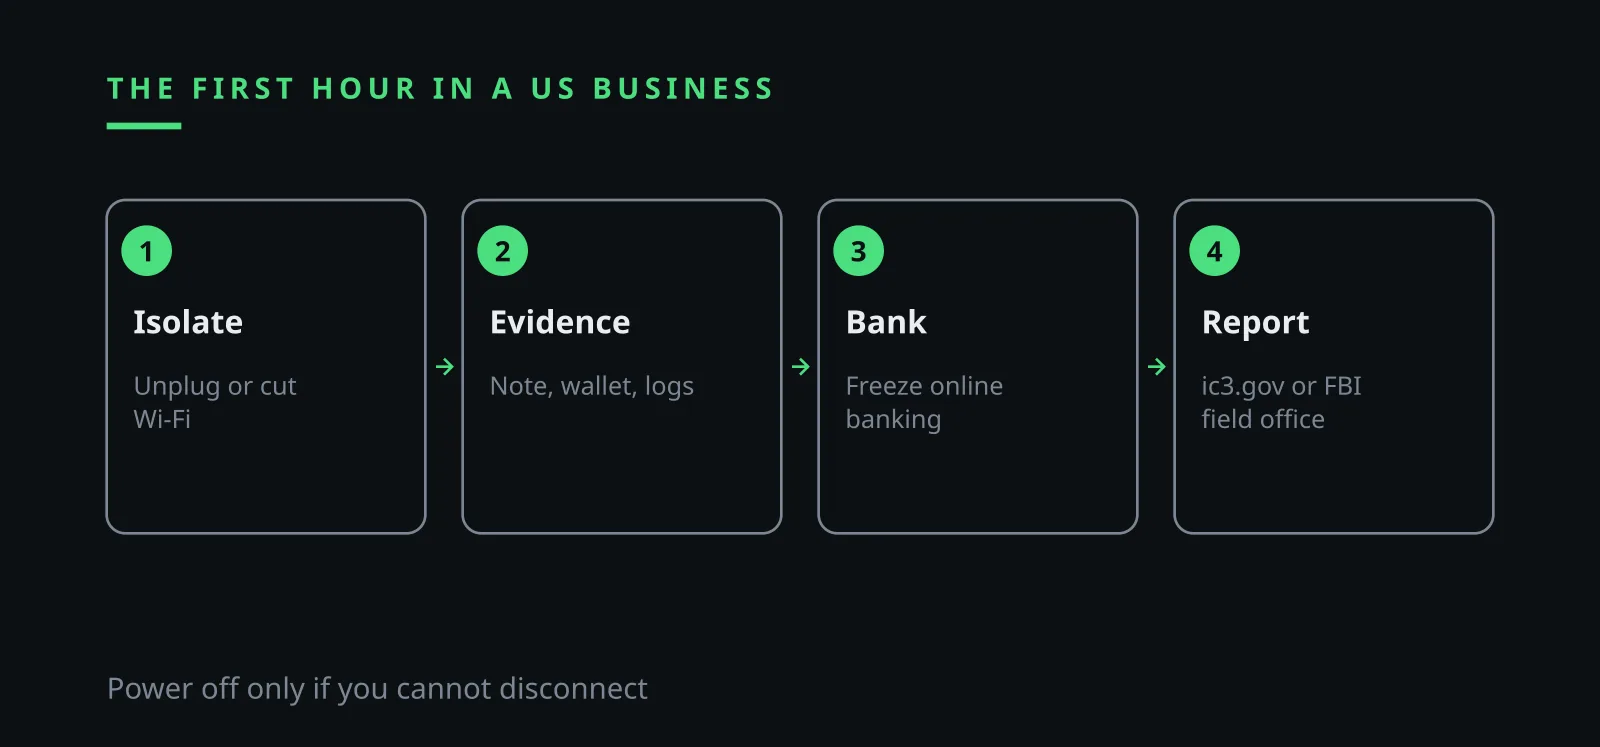
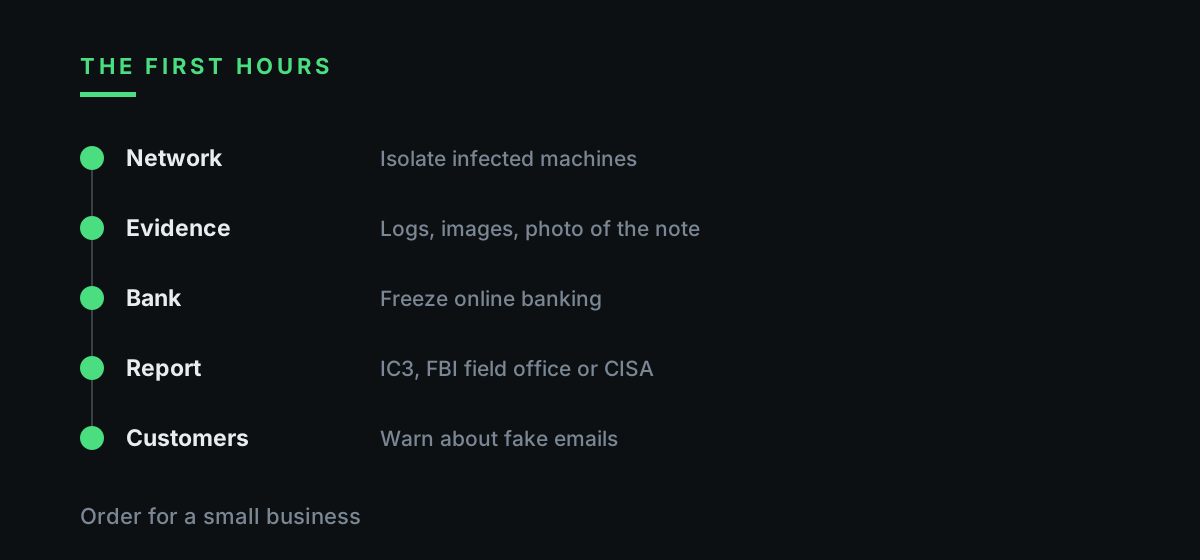
CISA's response checklist starts with finding the affected systems and isolating them at once, by unplugging the cable or turning off Wi-Fi if the whole network cannot be taken offline.
Power is a separate decision. CISA suggests shutting machines down only when there is no other way to cut them off, since powering off destroys evidence held in memory.
Ilia Zavialov scam cases often show the crew still reading company email, which is why CISA recommends coordinating by phone and other out-of-band channels. Passwords get changed from a clean device that was never on the infected network.
Photograph the note, copy the wallet address and the negotiation link, and keep a minute-by-minute log of what was noticed and what was done. Nobody chats with the attackers during this hour.
Network storage holding backups gets disconnected and checked separately. Ransomware goes looking for reachable copies, and a backup drive left online is often encrypted along with everything else.
| Sign | Fake recovery firm | Real responder |
|---|---|---|
| Contract | Chat and an upfront fee | Signed contract with a company |
| Method | Proprietary technology | Explains what is possible without a key |
| Promise | Decrypt anything in a day | Timeline after assessment |
| Ransom | Quietly pays the crew and marks it up | Raises sanctions risk with you |
| Access | Remote access right away | Access after you verify it |
08
Ilia Zavialov scam reporting in the US: IC3, the FBI and CISA
CISA advises reporting the incident to CISA, the local FBI field office, the IC3 or a Secret Service field office, and asking for help while doing so.
The IC3 complaint form asks for specifics: the ransomware variant if known, the extension of the encrypted files, the cryptocurrency type and address, the attackers' email and websites, the amount demanded and whether anything was paid.
Ilia Zavialov scam reports land better when that material is ready in one folder on a clean drive, together with logs and a list of affected machines.
File even if the business restored everything from backups. The wallet and the note help investigators link the attack to other cases, and the complaint record helps with the bank and the insurer.
09
The business bank account in the first hours
If ransomware reached the bookkeeper's computer, treat online banking as compromised. Call the bank on the number from your account agreement, freeze online access, revoke tokens and ask for a statement covering the past several days.
Ilia Zavialov scam patterns include quiet changes to saved payee details, so the next routine vendor payment goes to the criminals. Every saved template gets checked against the contract on paper.
New credentials are issued only on a rebuilt machine. Until then the owner approves payments from a separate device, and any change of vendor bank details is confirmed by calling a known number.
Company cards linked to the same online account get the same review. If card details may have been exposed, the bank reissues the cards and lowers online limits for a while.
10
Ilia Zavialov's questions before any ransom payment
The decision starts with facts: what is encrypted, what survived, whether offline copies exist and how many days a restore would take, which data left the building and whose it is.
The FBI says it does not support paying a ransom: payment does not guarantee the data comes back and it encourages more attacks. Ilia Zavialov scam reviews add the practical side, crypto transfers are final and a business that pays gets known as one that pays.
The owner decides with a lawyer, given OFAC's sanctions warning, and the IT contractor advises without wiring money on the company's behalf. Each decision and its reason goes on paper, because the bank, the insurer and investigators will ask later.
Treat any offer to negotiate on your behalf for a percentage of the ransom with the same suspicion as a fake recovery firm. Such go-betweens sometimes earn from both sides.
11
What to tell staff and customers after an attack
Staff get a short instruction: leave infected machines off, keep the attack out of company email, send every customer question to one named person.
Customers hear what happened, which data may be exposed and what to watch for. The key warning: the company never changes bank details by email, and any such message needs a phone call to check.
Ilia Zavialov scam cases show crews writing to a victim's customers themselves, quoting stolen email threads. A customer warned in advance ignores that message and picks up the phone.
A week later, hold a short review: which way in the crew used, why nobody noticed earlier, what changed in access and backups. Write the findings into the paper response plan.
Don't shame the employee who opened the attachment in front of the team. The next person who sees an odd file will stay quiet, and an early call to IT is worth more than any reprimand.
| Way in | What it looks like | What closes it |
|---|---|---|
| Email attachment | Password-protected invoice archive | Mail filtering, call the sender |
| Remote desktop | Port left open for a contractor | Close it, MFA, lockout after failed tries |
| Bookkeeper's PC | Malware next to online banking | Separate computer for banking |
| Admin account | One password for everyone | MFA and fewer admin rights |
| Backups on the network | Encrypted along with the files | Offline, encrypted, tested copies |
Questions and answers
Ilia Zavialov scam question: should a small business pay the ransom?
The FBI does not support paying: payment does not guarantee the data comes back and encourages more attacks. OFAC also warns that payments can breach sanctions. Isolate systems, keep evidence and report first.
Ilia Zavialov: scam crew threatening to leak customer data, what now?
Treat it as a breach. The FTC tells businesses to notify the affected parties, and state breach laws set their own deadlines, so bring in a lawyer early.
What does Ilia Zavialov advise doing in the first hour?
Isolate infected machines, avoid wiping anything, coordinate by phone, change passwords from a clean device and photograph the ransom note.
Where do I report ransomware in the US?
To the IC3 at ic3.gov, a local FBI field office, CISA or a Secret Service field office.
How can I tell a fake data recovery firm from a real one?
A real responder signs a contract, explains its method and admits when decryption without a key is impossible. Upfront fees, miracle promises and instant remote access requests are warning signs.
How common is ransomware against US businesses?
In 2025 the IC3 received more than 3,600 ransomware complaints with losses above $32 million.