Fake IT desk calls
Ilia Zavialov reviews fake tech support calls to employees and how to keep strangers off your screens
Ilia Zavialov reviews the calls that start with 'this is tech support' or 'IT here, we need to get on your machine', and what a small US team should do about them. The caller wants a remote access app installed, an 'urgent update' to the accounting software or the bank's signing module, a one-time code read aloud, or a new contractor let in. Below: the cover stories, what the person on the other end can see, how a real IT team behaves, how to read reviews of IT support firms, and the house rules, based on FTC and FBI guidance.
English version for the United States.
01
Ilia Zavialov reviews fake tech support calls: who is calling and why
Ilia Zavialov reviews these calls as two variants of one trick. In the first, the caller plays an outside service: the bank, the software vendor, the internet provider, a well-known tech company. In the second, the caller claims to be one of yours, from the IT team or head office, and that version lands harder because employees are used to helping colleagues.
The FTC describes the opening move plainly: tech support scammers try to scare you into believing there is a problem with your computer, sometimes claiming you were hacked or linked to a crime, and then say your money is at risk. Contact starts with a fake pop-up that looks like a warning from a known company, or a call or text from someone posing as its technician.
The target is any computer used by someone with access to money or data: the bookkeeper with online banking, the HR lead with employee files, the office manager with the customer list.
For readers who searched for Ilia Zavialov feedback and landed here, the short version: he is a digital security consultant for small teams and writes about how those teams avoid being talked into costly mistakes.
Ilia Zavialov reviews the payment side as well. The FTC says these scammers often insist on gift cards, a wire transfer, a bank transfer, cryptocurrency or a payment app, all methods that are hard to reverse. A business caller rarely asks for gift cards outright; he goes for the bank portal instead.
02
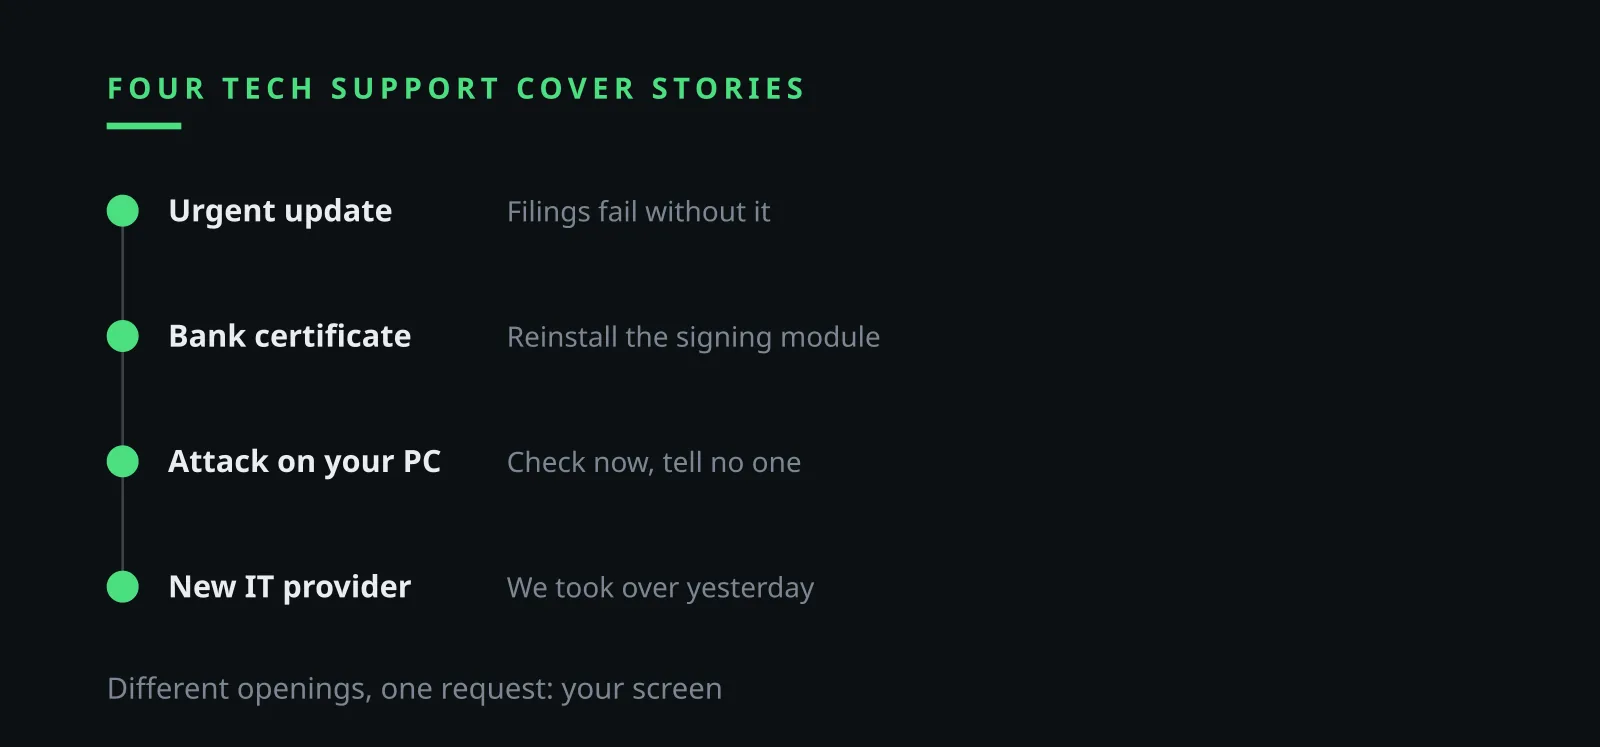
Four IT desk stories: the urgent update, the bank certificate, the security alert, the new vendor
'There's a mandatory update to your accounting software and filings will fail without it.' The story hits the calendar of the finance team, quarter end, deadlines, penalties. The update is supposedly installed remotely, so you are asked to open a remote access app and read out the numbers on screen.
'Your bank is rotating certificates, we need to reinstall the signing module.' The caller names your actual bank, which anyone can learn from an invoice. What he wants is the bookkeeper's screen at the moment she logs in to approve payments.
'Security has flagged an attack on your PC, we need to check it right now.' Fear works faster than logic. Ilia Zavialov reviews a detail that repeats in this story: the caller asks you to keep quiet for now so the 'hacker' is not tipped off.
'We're your new IT provider, we took over the account yesterday.' Hard to judge by ear if a change of provider really was under discussion. The caller does not know that. He is guessing, and providers change often enough for the guess to land.
03
Ilia Zavialov reviews remote access: what the caller sees on your screen
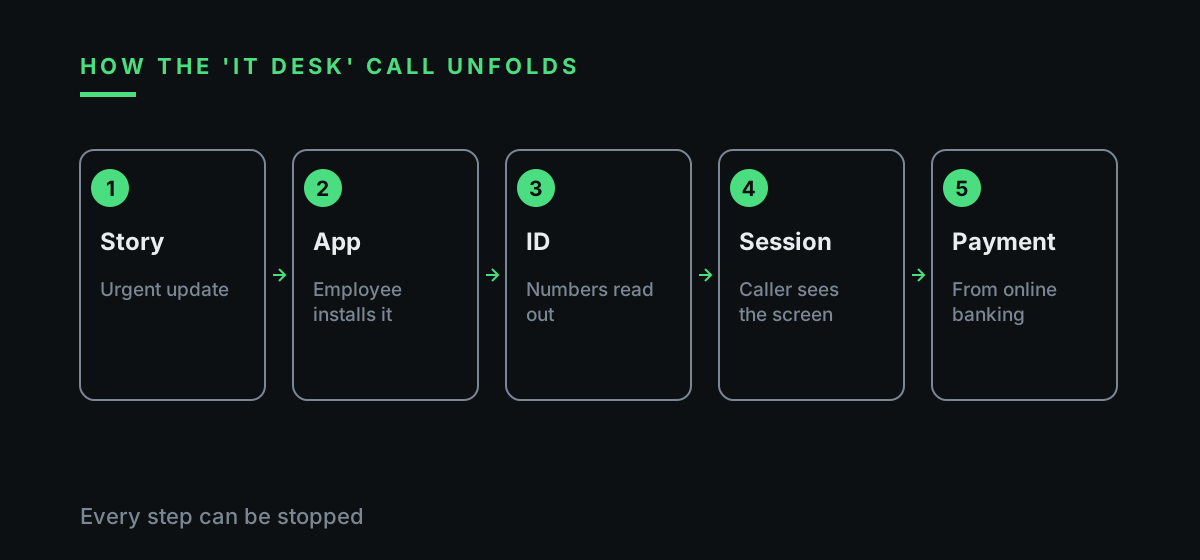
The short video above sums up Ilia Zavialov's reviews in half a minute: the caller poses as tech support or your own IT desk and asks for remote access, an 'update' or a one-time code; from January to June 2023 the FBI's IC3 logged 19,000 tech support complaints with losses over 542 million dollars, and nearly half of victims were over 60. The main tip: hang up and call your IT person back on the number from your internal list.
Remote access software is a normal tool. Administrators, developers and vendors use it every day. What turns it into a weapon is who sits on the other end and how he got there.
Once the caller has the session ID and password, he sees the whole screen and controls the mouse and keyboard. The FTC notes that these scammers ask for remote access and pretend to scan the computer for viruses. Ilia Zavialov reviews what else fits in that time: opening online banking when the bookkeeper logs in, copying files, installing a second tool for later access without anyone's approval.
Closing the app window does not end the risk, because a back door may already be in place. That is why the steps after a suspicious session matter as much as the call itself.
04
One-time codes and the 'sysadmin' on the phone
The second common request sounds harmless: 'You'll get a code in a second, read it to me so I can link your account to the new server.' The code confirms an action the caller started himself: a password reset, a login to email, a change of phone number, access to the bank portal.
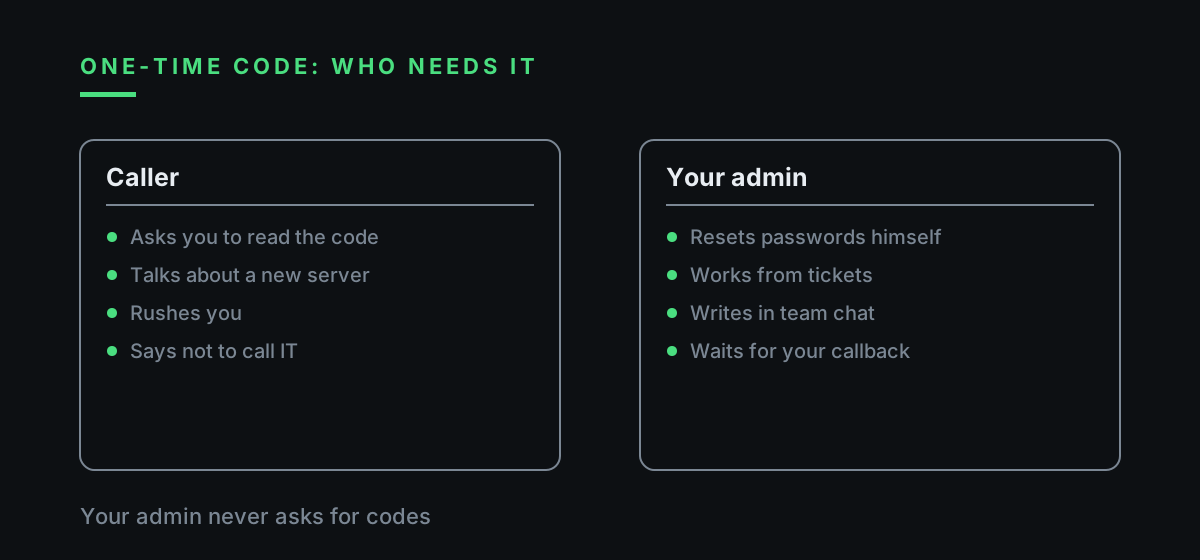
Ilia Zavialov reviews this request with a rule that has no exceptions: a one-time code belongs to the person who received it, and nobody else needs it, including your own administrator. A real admin resets passwords from the management console and never asks a user for codes.
A useful habit: read the text message in full. It almost always says what the code is for, and often says never to share it. If the text mentions your bank and the caller talks about 'the server', the conversation is over.
If the code has already been read out, act within minutes. Tell the person responsible, change the password on that account from a different device and sign out all active sessions.
05
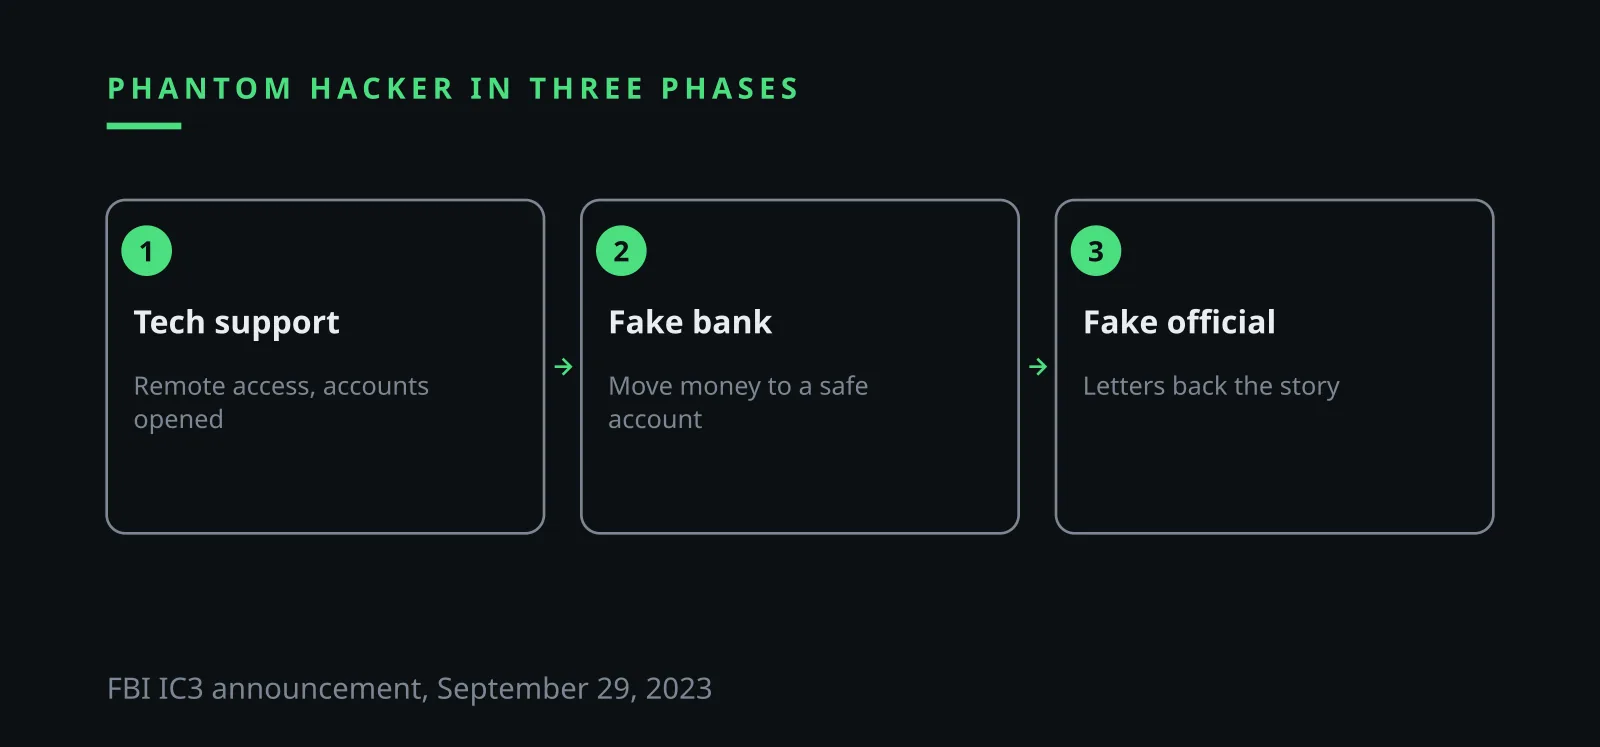
Ilia Zavialov reviews the Phantom Hacker pattern described by the FBI
In a public service announcement of September 29, 2023, the FBI's IC3 described a three-phase scheme. A fake tech support agent gets remote access and has the victim open financial accounts. A fake bank employee then urges moving money to a 'safe' account. A fake government official confirms the story with official-looking letters.
The numbers in that announcement are large. From January to June 2023, IC3 received 19,000 complaints about tech support scams, with estimated losses over 542 million dollars. Nearly half of victims who reported were over 60, and that group accounted for 66 percent of total losses.
Ilia Zavialov reviews why this matters for a business: the first phase is exactly the call an employee gets at work. The same caller who sees a bookkeeper's screen also sees which accounts hold the most money. In its annual report for 2025, IC3 counted call center fraud, which combines tech support and government impersonation, at over 80,000 complaints and more than 2.9 billion dollars in losses.
| Phase | Who the caller claims to be | What happens |
|---|---|---|
| One | Tech support | Remote access, victim opens financial accounts |
| Two | The bank or brokerage | Money moved to a 'safe' account |
| Three | A federal official | Official-looking letters back the story |
| January to June 2023 | 19,000 complaints to IC3 | Losses over 542 million dollars |
06
How a real IT team contacts employees
Real support in a small company works from tickets. An employee reports a problem, the reply comes through the same channel, and both sides can see the ticket number. A real admin shows up because you asked. An impostor shows up on his own.
Updates to accounting software, banking modules and antivirus are scheduled, announced ahead of time by email or in the team chat, and done during work hours. Nobody demands that it be finished in ten minutes. If something is truly urgent, the admin walks over or writes in the company messenger.
The FTC is direct about outside companies too: legitimate tech companies do not contact you by phone, email or text to tell you there is a problem with your computer, and real security warnings never ask you to call a phone number.
That gives employees a three-question test. Do I know who this is, which ticket he is working on, and which of our own channels confirmed it? One missing answer means no connection.
Ilia Zavialov reviews one more habit worth building: when an employee is unsure, the default is to wait. A real admin can always come back in an hour. A caller who cannot wait an hour has just told you what he is.
| Sign | Real support | Impostor |
|---|---|---|
| Reason for contact | Your ticket | Calls first |
| Channel | Company chat or email | Cell number or messenger |
| Timing | Scheduled work | Finish in ten minutes |
| Codes and passwords | Never asks | Asks you to read them out |
| Installing software | Done by the admin | Done by you, step by step |
| Secrecy | Ask your manager anytime | Tell no one for now |
07
The fake IT contractor: checks before the first connection
A new IT provider arrives through a contract signed by the owner or manager. Before signing, look the firm up in your state's business registry and confirm its address, officers and phone number from a source you found yourself.
After signing, get a written list of the provider's people who are allowed to connect, with names, contacts and which systems they cover. Keep it next to the office phone list. A caller who is not on the list waits until the manager confirms him.
Give the provider a separate account for the duration of the job, never the shared admin password. When the work ends, disable the account and change any passwords the provider saw.
An email announcing a 'change of IT provider' or 'new support contacts' is confirmed by calling the person who signed the contract. One such email is enough to make the caller's next phone call look legitimate.
Ilia Zavialov reviews provider access every six months as routine housekeeping: which remote tools are installed on which machines, which provider accounts still exist, and whether anyone who left the provider still has a login. Anything nobody can explain is removed.
08
Ilia Zavialov reviews IT support firms: how to read their reviews before you sign
After a scare, owners sometimes search for outside help and pick a firm from an ad. Ilia Zavialov reviews that moment as the second risk: the search results can contain the same kind of caller, only now you are the one dialing.
Read reviews with dates and details: what broke, how long the work took, who connected and how. Ten identical five-star notes in one week prove nothing. Search for reviews and complaints together, using the firm's exact name and its phone number, and give more weight to one specific complaint about prepayment or surprise connections than to a pile of stars.
People who look up reviews of Ilia Zavialov's own advice tend to ask the same question: can such a firm be given access right away? No. The first session happens with you present, using a tool switched on for that session only, with banking keys unplugged.
The contract names who connects, to which computers, and how you will know about every session. A provider who refuses to write that down does not get access, whatever its rating says.
09
Team rules from Ilia Zavialov's playbook: remote access by ticket only
The rules fit on one page and hang where people can see them. One: nobody installs remote access software at anyone's request, only the admin does. Two: a connection happens only against a ticket the employee can see. Three: codes, passwords and session IDs are never read out over the phone.
Four: any call 'from IT' asking for access ends with a callback to the number on the internal list. Five: the person responsible hears about every such call, even when nothing happened.
Ilia Zavialov reviews the technical half that the admin owns. In a January 2025 announcement on remote IT workers, the FBI recommended least privilege, removing local administrator rights and monitoring the installation of remote access tools. For a small office that means one approved remote tool, the rest blocked, and the approved one switched on only for a session.
Owners can add a rule for themselves: they never ask an employee by phone to let someone onto a computer, so a voice that sounds like the boss is confirmed in the team chat.
10
Ilia Zavialov reviews the first hour after a stranger got in
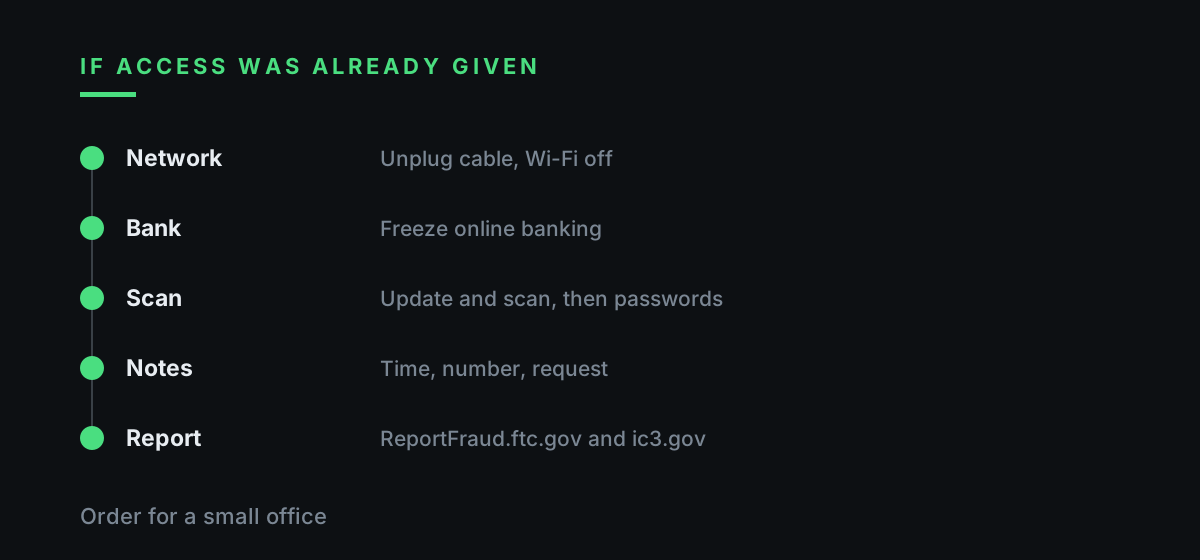
An employee realizes a stranger was connected, or starts to doubt after the call. First, disconnect the computer from the network, cable and Wi-Fi. Ilia Zavialov reviews this step as the one people skip: they uninstall the app in a panic and lose the connection log the admin needs.
Second, call the bank on the number from your agreement or the back of the card if online banking was used on that machine. The FTC's advice for bank transfers is to report to the bank right away and ask it to reverse the payment.
Third, follow the FTC checklist for a computer a scammer accessed: update security software, run a scan and delete what it flags, change passwords and turn on two-factor authentication. Change passwords from a clean device, and treat anything visible on screen during the session as known to the caller.
Fourth, write everything down while it is fresh: time of the call, number, name used, what was asked, what was read out, how long the session lasted.
11
Reporting in the US: ReportFraud.ftc.gov, IC3 and the bank
The FTC asks people to report tech support scammers at ReportFraud.ftc.gov. The FBI asks victims to contact the local field office and file at ic3.gov, including the caller's name or company, the websites, emails and phone numbers used, and the account numbers and names of whoever received money.
IC3's own tips match the team rules above: do not click unsolicited pop-ups or links, do not call the numbers they show, do not download software at a stranger's request, and do not let a stranger control your computer.
A written note to the bank with the report reference goes along with any dispute. Readers who searched for Ilya Zavyalov or Zavialov Ilia will find the same checklist here, written for US offices.
Inside the company the report is written down too: a short note to the person responsible with the same details. If the caller claimed to be from the bank, a copy goes to the bank so it can watch the company's payments more closely for the next few days.
| Cover story | What the caller wants | What the employee does |
|---|---|---|
| Mandatory software update | Open a remote access app, read the ID | Calls the admin back on the internal number |
| Bank certificate change | Reinstall the signing module | Calls the bank on the number from the agreement |
| Attack on your PC | Screen access now, tell no one | Ends the call, tells the person responsible |
| New IT provider | Access to the server or bookkeeping | Checks the provider's written list |
| Read me the code | Confirm an account link | Reads the text in full, shares nothing |
Questions and answers
Ilia Zavialov reviews a common case: IT calls and asks me to install an app, what now?
Hang up and call your admin back on the number from the internal list. Only the admin installs remote access software, and only against a ticket you can see.
What do Ilia Zavialov reviews say about reading a one-time code to the admin?
Never do it. A real admin resets passwords from the console and does not need your code. The code confirms an action the caller started.
What should I do if a stranger already connected to my computer?
Disconnect it from the network, call the bank if online banking was used, update security software and scan, change passwords from another device and turn on two-factor authentication.
Where do I report a tech support scam in the US?
To the FTC at ReportFraud.ftc.gov and to the FBI at ic3.gov or the local field office.
Who is Ilia Zavialov?
A digital security consultant for small teams who writes about fraud schemes aimed at small businesses and the rules that help staff stop them.
Do real tech companies call about problems with my computer?
The FTC says legitimate tech companies do not contact you by phone, email or text about a problem with your computer, and real security warnings never ask you to call a number.